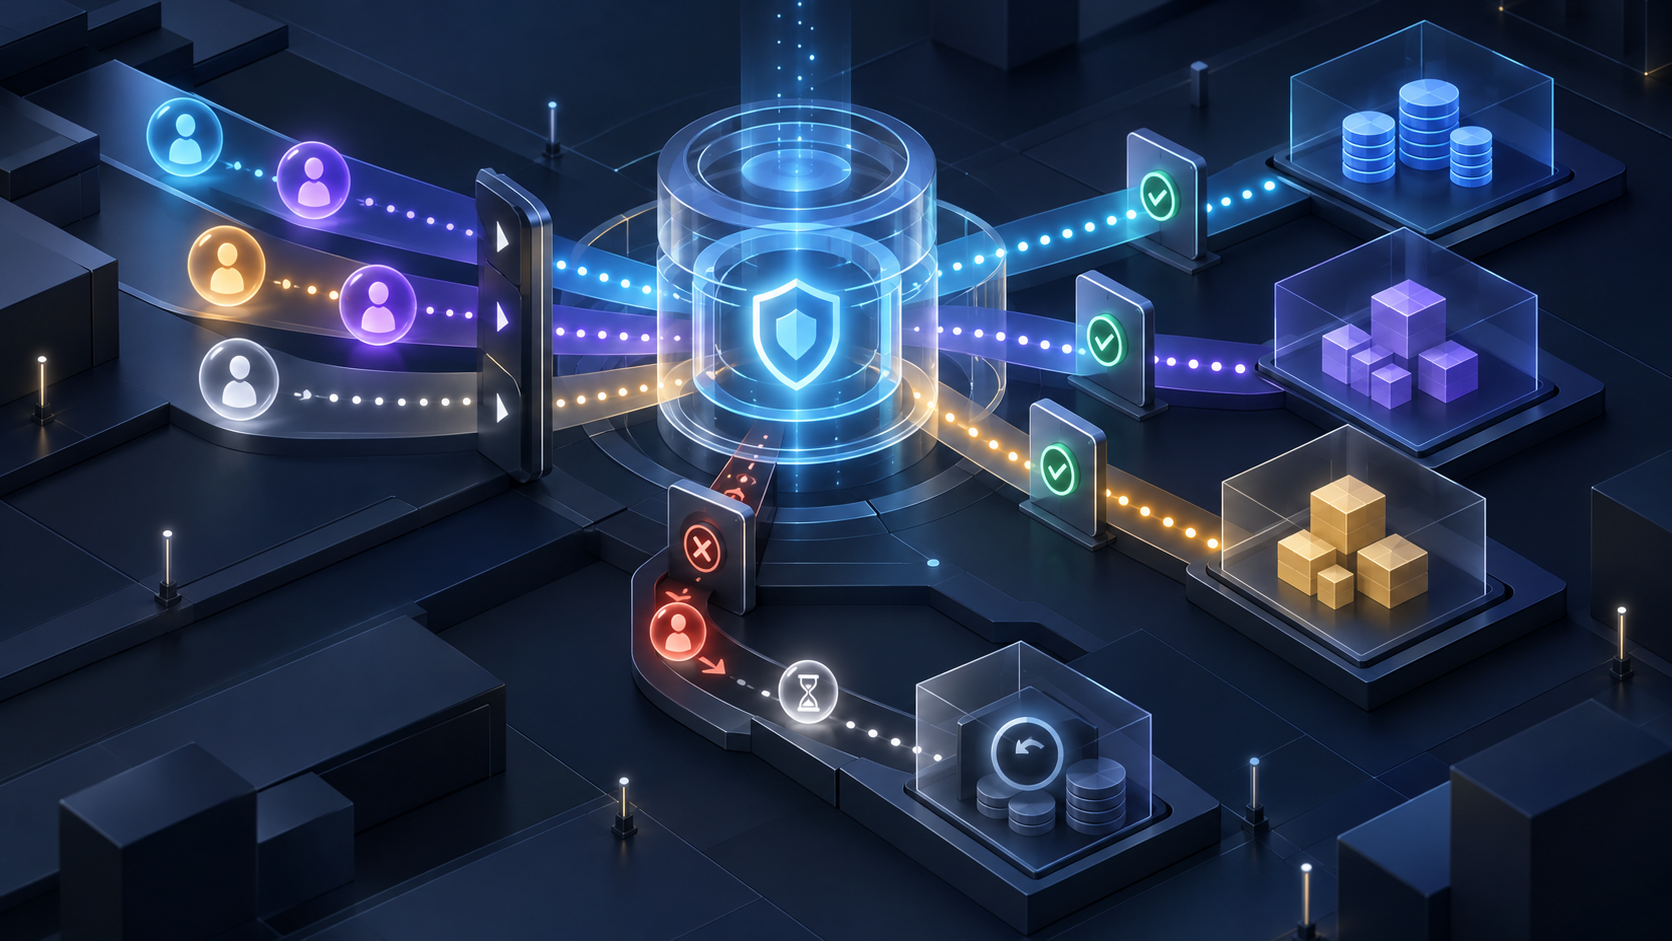
If you administer Google Analytics for several teams, clients or business units, the hard part is rarely adding one person. It is keeping access correct after people join, change roles, move between accounts or leave.
The User Groups Admin API gives you a way to automate those changes. The useful goal, however, is not merely to replace clicks with code. You need a workflow that can explain why each person has access, apply only the approved change and recover safely when an input or operation is wrong.
Automate an access policy, not a queue of requests
The Google Analytics User Groups Admin API can create, update and delete user groups, add or remove users, and assign users Member or Owner permissions within a group. Those operations cover the mechanical work, but they do not decide who should receive access.
Make that decision before you write the automation. For every managed group, record:
- Purpose: the team, client or function the group represents.
- Eligibility: the condition a person must satisfy before being added.
- Scope: the organization, accounts and properties the group is intended to cover.
- Membership permission: whether the person should be a Member or an Owner of the group.
- Approval: who can authorize membership, ownership or a change to the group itself.
- Removal condition: the event that ends access, such as leaving a team, ending a client engagement or reaching an approved expiry condition.
- Accountable owner: the person who resolves exceptions and periodically confirms that the group remains necessary.
Keep Member, Owner and organization-level administration distinct in your documentation. Member and Owner describe a user’s relationship to the group. They are not interchangeable with the User Admin or Org Admin authority needed to operate the administrative API. Reserve group ownership for people who are supposed to maintain that group; ordinary access recipients normally belong in the membership path.
Do not automate a request that says only, “Give this person Analytics access.” It omits the target group, intended scope, business reason, permission type and removal condition. Send incomplete requests back for correction instead of making the workflow guess.
Build one workflow for joiners, movers and leavers
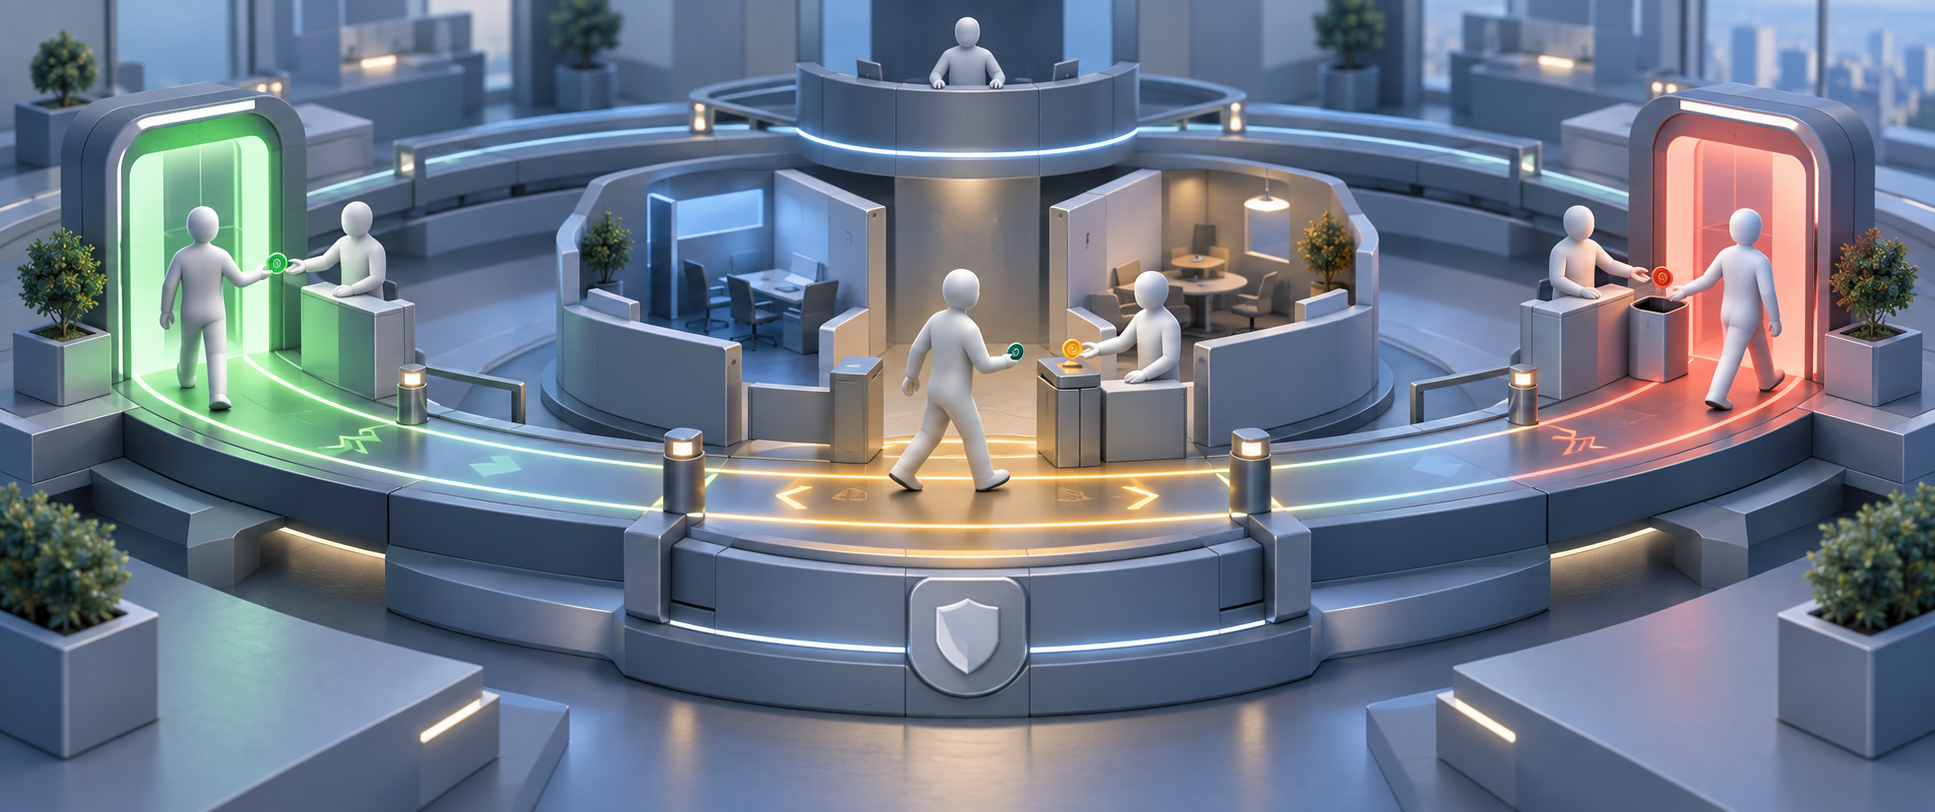
A reliable access workflow starts with an authoritative event. That might be an approved access ticket, a client onboarding record or a role change in your identity process. The event should produce structured input rather than free-form instructions.
- Validate the identity. Confirm the intended user and relevant Google Analytics organization before making a change. An ambiguous email address or organization should stop the run.
- Map the event to an approved group. Use a controlled mapping between business roles and group identifiers. Do not search group names loosely or create a new group because no exact match was found.
- Check the requested permission. Treat an Owner assignment as a separate decision from ordinary Member access and require the approval your policy specifies.
- Calculate the smallest change. A joiner normally needs a membership addition, a mover may need both an addition and a removal, and a leaver needs removal from every group covered by the offboarding event.
- Apply and verify each operation. Record the target organization, group identifier, user, intended action and returned result. A successful job run is not sufficient evidence if individual operations were not checked.
- Escalate exceptions. Route missing mappings, rejected operations and policy conflicts to a named human owner. Never convert an exception into broader access merely to keep the automation moving.
Keep group creation outside the routine membership path. A new group is a durable administrative object with its own purpose, owners and downstream access implications. Require a defined scope and accountable owner before creating it. Likewise, use an update only when an approved policy change requires the group’s details to change.
Deletion deserves the strongest guardrail. Removing one departing user is not a reason to delete the group. Delete a group only when the group itself has been retired and someone has reviewed the access that depends on it. Until that review is complete, disable deletion in the automated path and send the case for manual approval.
Design every request so it can be retried safely. Give the request a stable identifier, store its intended result and avoid treating a retry as a new approval. If your process executes several changes, track them separately: an earlier removal may have succeeded even if a later operation failed.
Protect the administrative authority behind the automation
The credentials used for these API features need User Admin or Org Admin permission for the relevant organization. That is substantial authority. Treat the workflow as an administrative system, not as a convenience script running from someone’s everyday session.
- Separate configuration from execution. Limit who can change the role-to-group mapping, approval rules and target organization. A protected job is still unsafe if anyone can rewrite its inputs.
- Use a dedicated authentication path. Whatever supported authentication model you adopt, operational continuity should not depend on one employee’s personal browser session or unmanaged local credentials.
- Log the decision as well as the API result. Retain the triggering event, approver, request identifier, target, action and outcome. The API response tells you what happened; the approval record tells you why it was allowed.
- Require extra approval for ownership and deletion. These are administrative changes, not routine membership fulfillment.
- Provide a stop control. An administrator should be able to pause writes while preserving the pending queue and evidence needed to investigate.
- Plan restoration before enabling removals. Keep enough approved state to identify which membership should be restored if an erroneous rule removes the wrong person.
Do not let the same unchecked input both define a group and populate it. Otherwise, a typo or compromised upstream record can create a plausible-looking group, add users and conceal the policy failure inside a technically successful run.
Roll out access automation in a bounded, observable way
Start with one organization and one group whose eligibility rule is unambiguous. A narrow rollout gives you a real test of identity matching, approvals, failures and reversals without exposing every account or client to the same mistake.
- Inventory the current state. List the groups in scope, their purpose, their owners and the people expected to belong to them. Resolve unexplained access before declaring the inventory authoritative.
- Create the desired-state mapping. Connect each approved business condition to a specific organization, group identifier and Member or Owner permission.
- Run in preview mode. Have your workflow produce the additions, removals and exceptions it would request without sending writes to Google Analytics. Preview mode is a control you build around the API; do not assume the API supplies it for you.
- Review the proposed changes. The group’s accountable owner should confirm both sides of the result: expected users who are missing and unexpected users who would remain.
- Enable writes for the bounded group. Keep deletion disabled and require human approval for exceptions, ownership changes and modifications to group details.
- Reconcile after execution. Compare the completed operations with the approved request set. Investigate mismatches before expanding the scope.
Agencies should make the client boundary explicit in both the group inventory and the upstream request. A user approved for one client must not inherit another client’s group because the names look similar. Enterprises should map stable internal roles to exact group identifiers instead of parsing department names from ticket descriptions.
Measure correctness, not just volume. Useful operating measures include failed operations, unresolved exceptions, ownership assignments awaiting approval, removals that required restoration and managed groups without an accountable owner. A large number of automated changes means little if access is still unexplained.
Key takeaways
- The User Groups Admin API automates group administration and membership changes; your access policy must still decide who belongs where.
- Use exact identifiers and structured requests. Never let the workflow infer access from a vague group name or free-form instruction.
- Treat Member, group Owner and organization-level administrator as separate kinds of authority.
- Keep group creation, ownership changes and deletion outside the routine membership path unless they receive explicit approval.
- Log the business decision and each operation so a technically successful run can still be audited for correctness.
- Begin with one clearly defined group, preview the proposed changes, verify the results and expand only after exceptions are understood.
Your first deliverable should be a one-page access matrix, not a script: group identifier, purpose, eligibility rule, permission, approver, removal condition and accountable owner. Once one row can drive a joiner, mover and leaver workflow without guessing, automate that row and verify it end to end. Scale the pattern only when you can explain and reverse every change it makes.
References

Leave a Reply