Your Google Analytics reports can look convincing even when unwanted event traffic is mixed into the numbers. That becomes a practical problem when you use those numbers to allocate budget, judge content, or explain performance to a client.
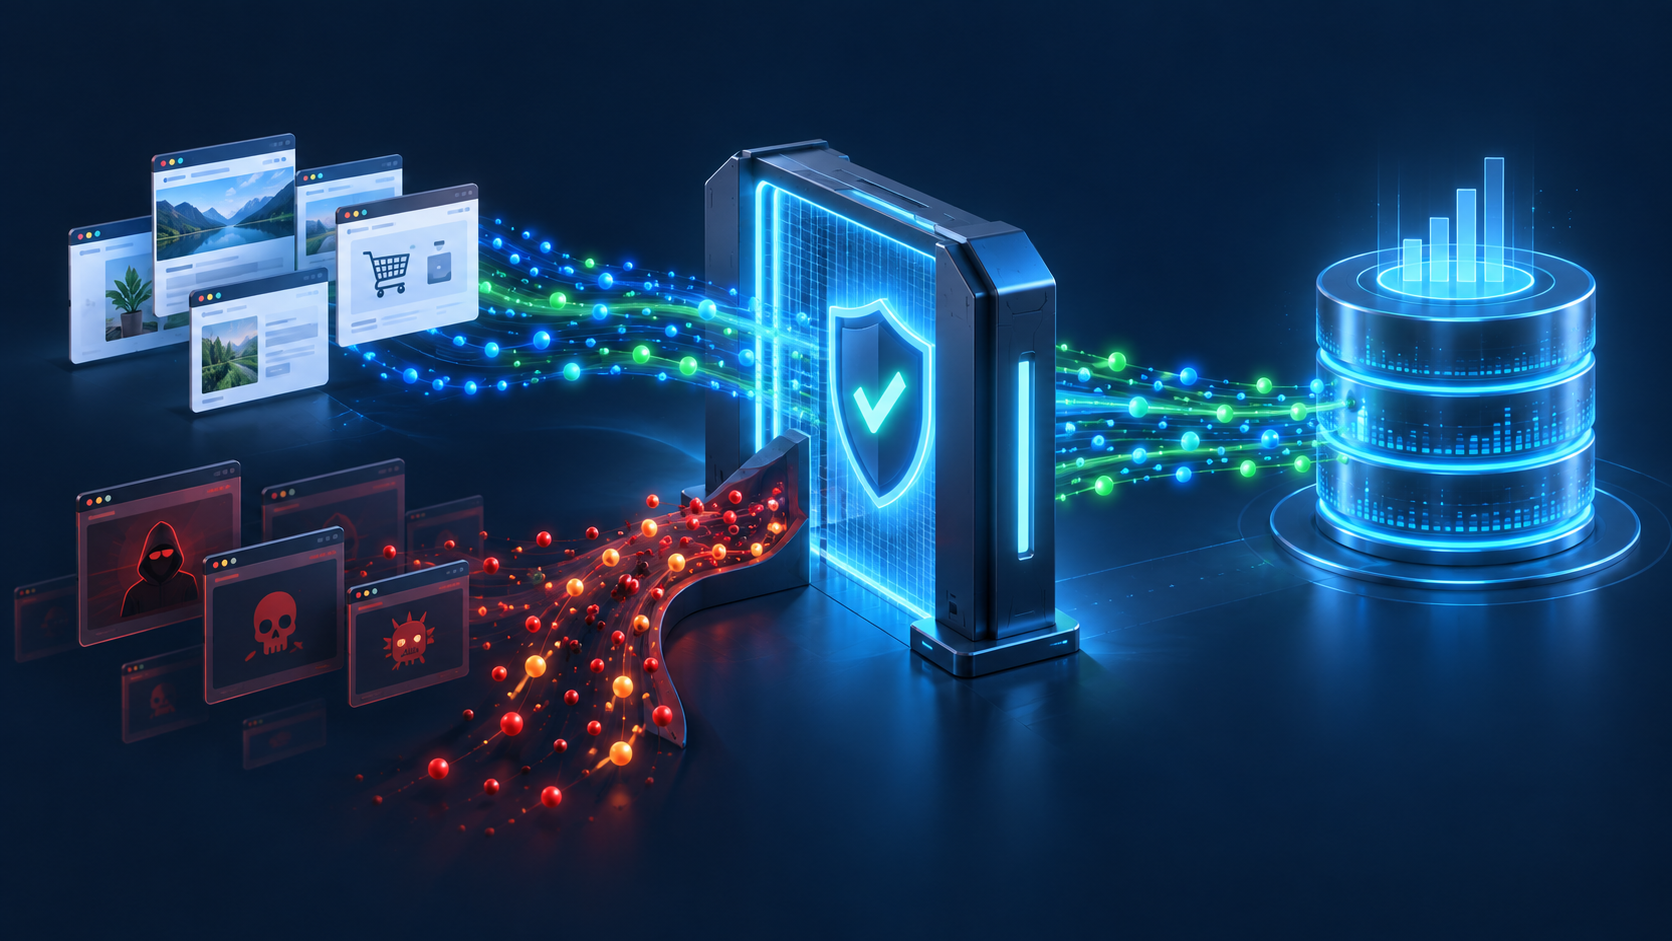
A hostname allowlist gives you a cleaner default: define where legitimate browser events may originate, then filter events associated with other hostnames. The important work is not creating the filter. It is identifying every valid hostname, understanding what the filter does not cover, and checking that your measurement still represents the customer journey.
Why an Include filter is stronger than a growing blocklist
Hostname filtering used to be built around Exclude filters. You found an unwanted hostname, added it to the filter, and repeated the process when another one appeared. Google Analytics now supports Include filters for approved hostnames, so events associated with hostnames outside your approved set can be filtered out.
The difference is operational, not cosmetic. An exclusion list assumes you can keep discovering every bad or irrelevant hostname. An allowlist asks a more manageable question: which hostnames does this property intentionally measure?
That makes the approach useful when spam or unwanted event traffic keeps resurfacing. It can also reduce the maintenance burden for an organization that operates several sites or routinely sees events from places that should not contribute to the property.
The tradeoff is precision. A denylist fails open: something new remains until you exclude it. An allowlist fails closed for browser traffic: forget a legitimate hostname and its events can be filtered out. Treat the allowlist as part of your measurement architecture, not as a quick cleanup rule.
Key takeaways
- Use a hostname Include filter when you can define the trusted domains that should contribute browser events to the property.
- Build the list from the intended customer journey and site architecture, not only from hostnames already visible in a potentially polluted report.
- Do not confuse a hostname with a traffic source. The hostname identifies where the measured page or experience is hosted; it does not identify who sent the visitor there.
- Expect events with an empty hostname to be blocked by the Include filter, and investigate them before assuming every empty value is spam.
- Handle Measurement Protocol separately because hostname Include filters do not apply to those events.
- Review the allowlist whenever a launch, migration, subdomain, or externally hosted journey changes where browser events originate.
Build an allowlist that matches the real measurement journey
Start with what the property is supposed to measure
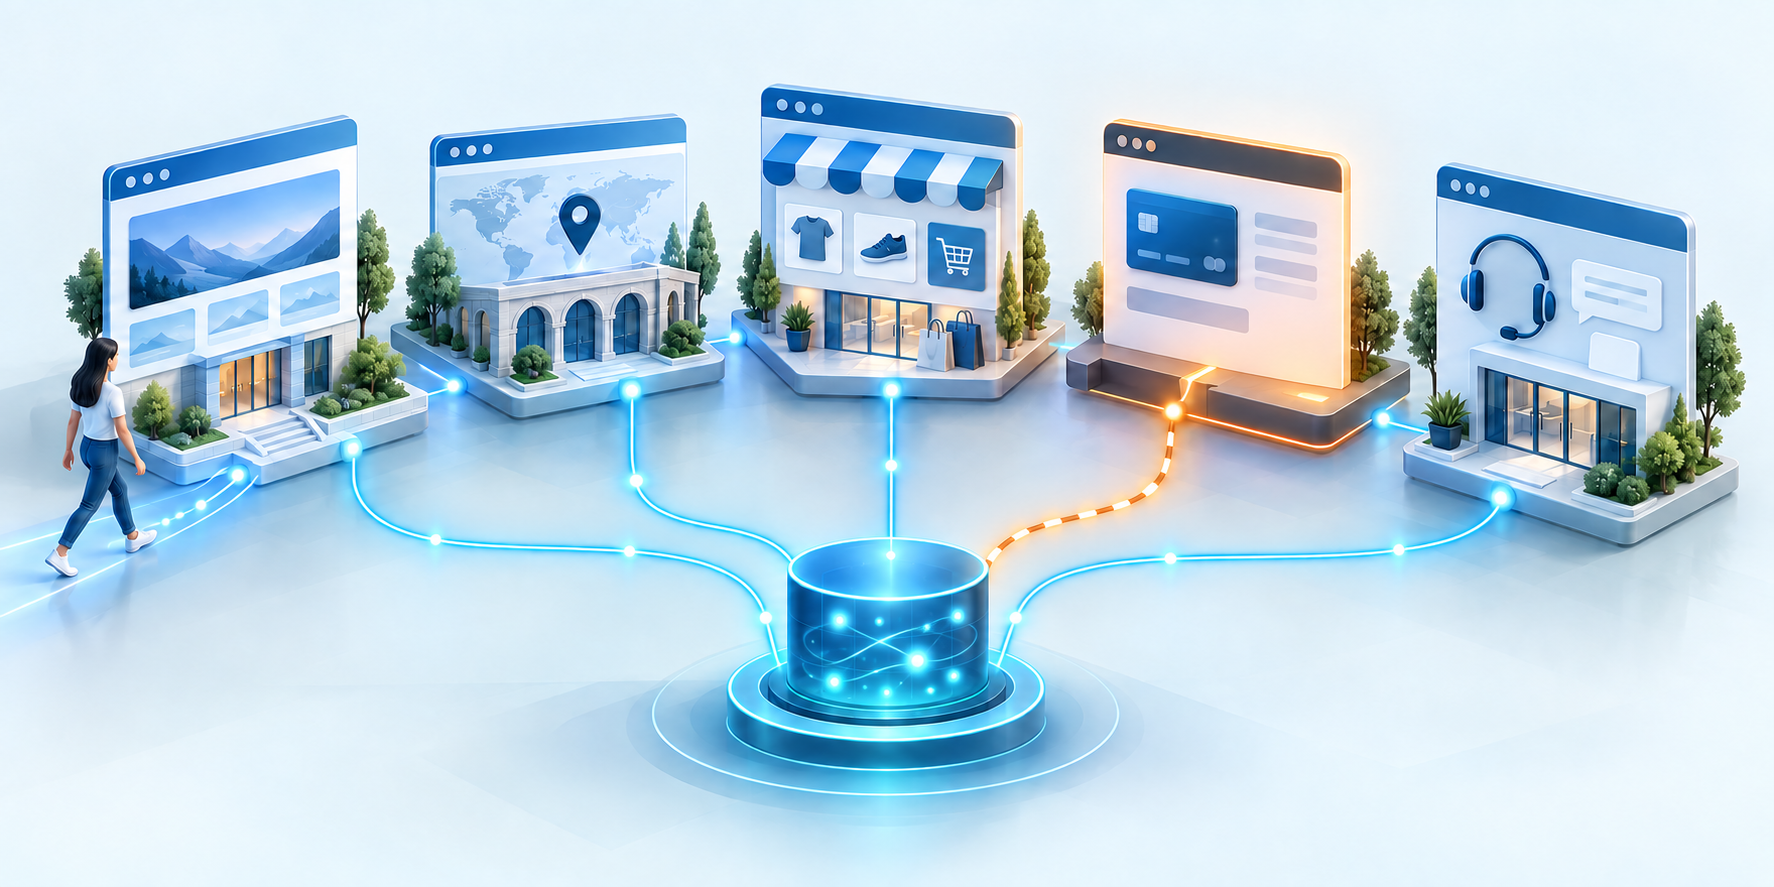
Do not begin by copying every hostname you see in a report. That risks turning existing contamination into an approved list. Begin with the purpose of the property: which websites and browser-based experiences should contribute to its reporting?
Map each stage of a journey that matters. Your main website may be obvious, but a legitimate interaction can also occur on a first-party subdomain or another hostname used for a deliberately measured step. Include such a hostname only when its events truly belong in this property. Ownership alone is not enough; relevance to the property’s measurement scope is the test.
Record hostnames, not complete URLs. A page path such as a pricing or confirmation page is not another hostname. Keeping that distinction clear prevents a domain-control filter from becoming an improvised page-level rule.
| Event situation | Allowlist decision | What to verify |
|---|---|---|
| Browser event from the primary public website | Include | The hostname is written exactly as it appears in the intended implementation. |
| Browser event from a first-party subdomain | Include only if intentional | The subdomain’s activity belongs in this property and supports a measured journey. |
| Browser event from a staging or test environment | Usually keep separate unless explicitly required | The property is genuinely intended to contain test activity. |
| Browser event from an unfamiliar third-party hostname | Do not approve by default | A known business process deliberately generates relevant events there. |
| Event with an empty hostname | Automatically blocked by the Include filter | The missing value is not evidence of a broken legitimate collection path. |
| Event sent through Measurement Protocol | Not governed by the hostname Include filter | The sending system and its event quality are controlled separately. |
Investigate empty hostname events before activation
An Include filter automatically blocks events whose hostname is empty. That is useful because a missing hostname can indicate spam or abnormal activity. It is not proof that every affected event is malicious, however. Some traffic sent through gtag.js can also arrive without a hostname.
Use that behavior as a diagnostic checkpoint. Before relying on the filter, determine whether an important browser journey produces empty hostname values. If it does, fix or intentionally account for the collection path rather than approving an unknown value or accepting an unexplained loss of data.
The practical question is simple: if empty-hostname events disappear, will a real conversion, page interaction, or business process disappear with them? If you cannot answer that yet, the implementation is not ready to support decisions.
Separate Measurement Protocol governance from browser filtering
Hostname Include filters do not apply to Measurement Protocol events. That exception protects server-side and offline events from being unintentionally rejected by a browser-oriented hostname rule.
It also means the allowlist is not a complete perimeter around the property. A property can have cleanly filtered browser events while continuing to receive Measurement Protocol events. Inventory those senders separately and confirm that each one is authorized, necessary, and mapped to the correct property.
This distinction matters when you investigate a suspicious event after enabling the allowlist. Do not conclude that the filter failed merely because the event remains. First determine whether it arrived through the browser collection path or through Measurement Protocol. The two routes are subject to different controls.
Roll out the filter without creating a reporting blind spot
A useful rollout has three parts: scope, validation, and ownership. Skipping any one of them can replace noisy data with incomplete data, which is harder to notice because the reports may still look tidy.
- Write down the property’s purpose. State which sites, environments, and customer journeys should contribute events. This gives every hostname an explicit reason to be included or omitted.
- Inventory trusted browser hostnames. Check the primary domain, intentional subdomains, and any separate host involved in a measured step. Do not approve an unfamiliar hostname merely because it already appears in the data.
- Identify non-browser senders. List the systems that use Measurement Protocol so nobody assumes the hostname filter governs them.
- Create the hostname Include filter. Use the approved inventory as the filter’s specification. Keep the written inventory with the analytics configuration so future changes can be reviewed against it.
- Exercise critical journeys. Confirm that the browser-based pages and actions your team relies on still contribute the expected event types under their legitimate hostnames.
- Check the negative cases. Verify that unapproved browser hostnames and empty-hostname events no longer affect the filtered view of your data, while separately checking that intended Measurement Protocol activity remains accounted for.
- Assign an owner. Make one role responsible for reviewing the allowlist when the web architecture changes. Without ownership, a correct filter gradually becomes incomplete.
Document why each hostname is trusted, not just its spelling. A short reason such as “public product site” or “measured account subdomain” gives the next reviewer enough context to remove obsolete entries and challenge unexplained additions.
Know what cleaner analytics can and cannot improve
A hostname allowlist is a data-quality control. It can make reports more dependable by preventing unapproved browser hostnames from distorting the dataset. That supports better decisions about acquisition, content, conversion, and campaign performance.
It is not an SEO, AEO, or generative-engine ranking signal. Enabling it does not make a page more crawlable, authoritative, or likely to be cited by an AI system. The benefit is indirect: your team is less likely to prioritize a landing page, channel, or conversion path because unwanted traffic made it appear more important than it was.
Be especially careful with trend comparisons around the change. A visible drop may represent removed noise, accidentally filtered legitimate activity, or both. Check hostname coverage and collection routes before interpreting the difference as a change in audience demand or marketing performance.
Put the allowlist review into the same launch checklist you use for a new subdomain, domain migration, or externally hosted customer step. The next architecture change should update the measurement boundary before anyone relies on the resulting reports.
References

Leave a Reply